

Regulatory Focus
Data Protection
Data Protection
195
Countries Covered
28
Languages
2367
Regulatory Sources
To take advantage of the significant opportunities the Internet of Things (IoT) presents, companies need to navigate the growing complexity of regulations across regulatory content such as data protection, cybersecurity and wireless.
Data protection and privacy regulations set forth rules relating to the protection of natural persons (individuals) with regard to the processing of personal data and rules relating to the free movement of personal data. They aim to make businesses more accountable for data privacy compliance and offer individuals greater rights and more control over their personal data.
Recent years have witnessed an unparalleled growth in data protection legislation, primarily as a knock-on effect from the sharp surge in mobile and consumer technologies. As a result, organizations have heightened burdens of compliance while handling large volumes of personal data.
In the EU, the General Data Protection Regulation (GDPR) (Regulation (EU) 2016/679), which entered into force on 25 May 2018, sets out the primary privacy framework. The GDPR extends the scope of the EU data protection law to all foreign companies processing data of EU residents and provides for harmonization of the data protection regulations throughout the EU.
In the US, various omnibus data protection bills have been enacted on the state level in recent years; however, no agreement has been reached yet on an overarching privacy law on a federal level.
This content covers the principal national data protection and privacy laws, regulations, mandatory standards, both proposed and enacted, globally, focusing on:
- Collection, storage and use of data
- Fair and lawful data processing
- Individual’s rights
- Sharing of data
- Data transfer to other countries
- Data classification and quality of data security measures
- Measures to ensure privacy in relation to connected products
In particular, the lawful processing of personal data is quickly becoming a priority for so-called “smart appliances”. Networked devices, capable of exchanging data, must be used in such a way as to protect users from the risk of privacy breaches. Accordingly, this content area also covers data protection implications for connected products.
Please note that we do not cover the following types of personal information: health information, financial/credit information, criminal records or data held by public entities. Our coverage also does not extend to regulations that apply only to electronic communications service providers (e.g. regulations regarding data retention by communications providers) or only to data brokers. Regulations on the use of biometric data by companies and related requirements fall under our coverage, whereas we do not cover regulations on biometric data that establish rules only for government entities, financial institutions and/or healthcare institutions.
Adherent’s coverage of data protection is historically comprehensive and includes, but is not limited to:
- EU: Protection of Individuals with Regard to the Processing of Personal Data and the Free Movement of Such Data, Regulation, (EU) 2016/679
- UK: Data Protection Act, 2018
- Norway: Personal Data Protection Act, No. 38, 2018
- Brazil: Protection of Personal Data, Law No. 13709/2018
- California (USA): Privacy of Personal Information, Assembly Bill 375, Enacted, 2018
- California (USA): Connected Devices, Privacy and Consumer Protection, Senate Bill 327 Enacted, 2018
- New Zealand: Privacy Act No. 31, 2020
- Canada: Personal Information Protection and Electronic Documents Act, 2000
- China: Personal Information Protection Law, 2021
- Kenya: Data Protection Act, No. 24, 2019
- India: Digital Personal Data Protection Act, 2023
We cover standards for our core products that are available from our partner Accuris. These are available through our Product Compliance Solution.
Connection with other regulatory content:
The Data Protection content captures regulations which focus on the processing of personal data. A connection with the Artificial Intelligence content might occur where, for example, personal data are used within AI systems. A connection with the Cybersecurity content may occur for regulations dealing with the security and certification of connected devices. The Data Protection content may also sometimes overlap with the Labor/Employment content.

Intelligent Resources
Automate the work of managing regulatory change.
Let AI agents do the heavy lifting of monitoring regulations, mapping requirements to products, extracting obligations, and surfacing the risks that need attention first.
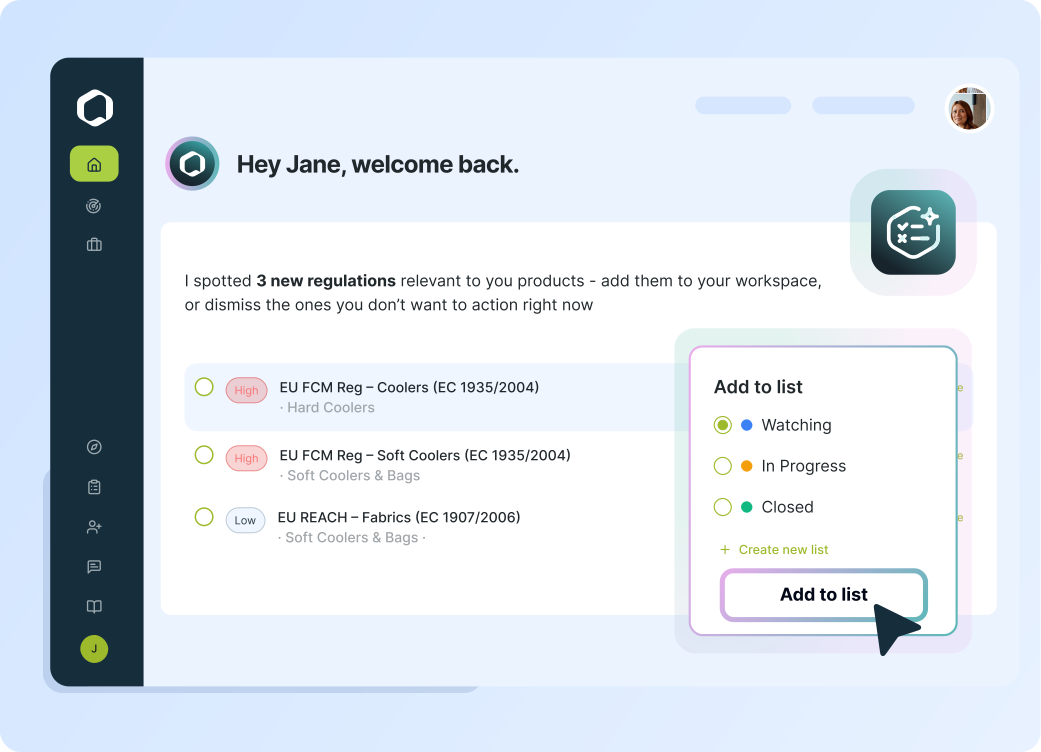
Monitor Product Compliance
Stay Ahead of Regulatory Change
Get early visibility into changes that could affect your products, supply chain, or market access—so you can act proactively, not reactively.
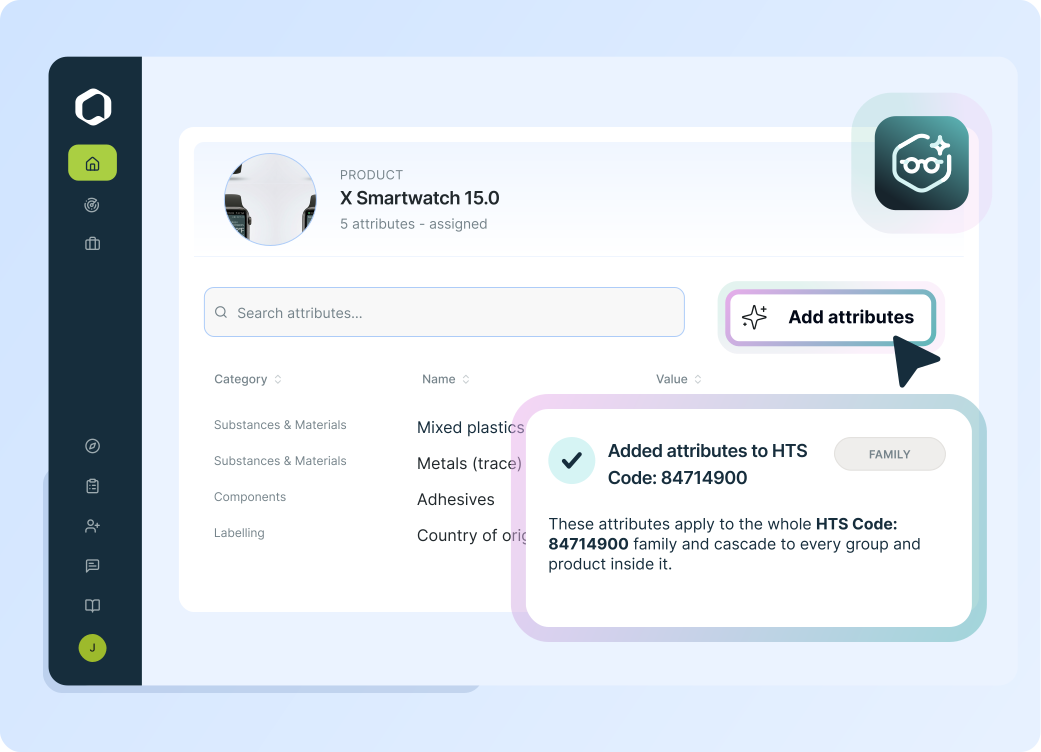
Assess Regulatory Applicability
Map Regulations to Your Products
Eliminate manual research and cut through regulatory noise by surfacing only the requirements relevant to your business, markets, and product categories.
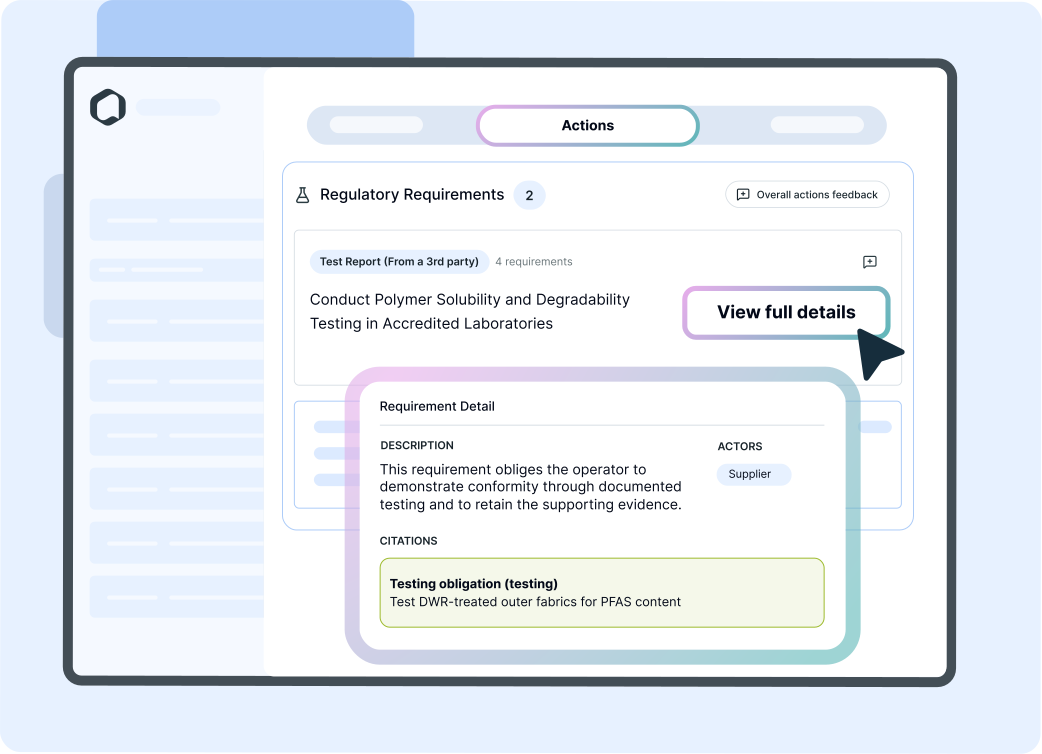
Identify Compliance Requirements
Turn complex regulations into clear, actionable tasks.
Give your teams instant clarity as AI agents transform dense legal and regulatory text into structured, easy-to-understand requirements.
Prioritize Business Risk
Focus Where Risk Is Highest
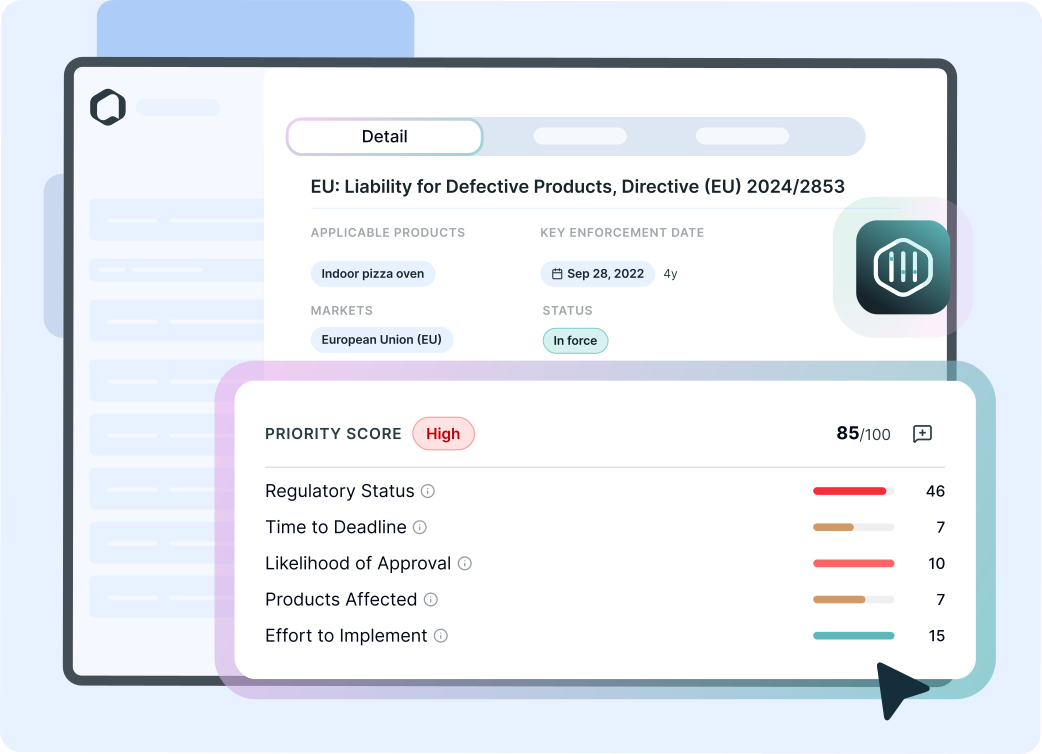
Make faster, risk-informed decisions with confidence as AI agents automatically rank regulatory changes based on urgency, business impact, compliance deadlines, and product exposure.
Spotlight
Turning Compliance into Value

The State of Product
Compliance 2026
Discover how 500+ global leaders are shifting product compliance from a cost-centre into a strategic driver of growth, with key benchmarks like 69% of teams calling remediation their biggest challenge.
Frequently Asked Questions
-
Organizations that process (collect, share, store, transfer, etc.) personal data of individuals are typically in scope – often regardless of where the organization is established. For example, laws such as the EU GDPR and Brazil’s LGPD, apply extraterritorially when activities involve offering goods or services to individuals or monitoring their behavior in the jurisdiction from which the law originates.
-
Companies must ensure lawful, fair, and transparent processing of personal data, respect and enable individuals’ rights (such as access, correction, and deletion), implement appropriate technical and organizational security measures, and manage cross-border data transfers in line with applicable safeguards and restrictions.
-
No. Consent is one lawful basis for personal data processing, but other bases may be more appropriate in certain cases – for example, performance of a contract, legal obligation, legitimate interests of an organisation, etc. It is also important to note that, according to many laws (including the EU GDPR), consent shall be freely given, specific, informed and unambiguous; and individuals have the right to withdraw consent at any time (although this does not affect the lawfulness of processing based on consent before its withdrawal).
-
Common penalties typically include administrative fines (sometimes tied to annual turnovers, such as under the EU GDPR) and corrective measures (e.g. orders to bring data processing into compliance, warnings, suspension of data processing or data transfers, and orders for deletion of personal data). In some jurisdictions, privacy law violations may result in criminal penalties and imprisonment. In addition, many countries allow individuals to bring civil actions against organisations, which can lead to damages being awarded.